In the world of cybersecurity and military defense, the weakest link is rarely the firewall, the encryption algorithm, or the physical barrier. It is the human being. Social engineering is the art and science of manipulating people into violating security protocols, revealing sensitive information, or performing actions that compromise themselves, their organizations, or their nations. Unlike technical hacking, which exploits code, social engineering exploits trust, fear, authority, urgency, and the natural human desire to be helpful.
From a military and defense perspective, social engineering is not a minor vulnerability — it is a primary attack vector for intelligence services, insurgent groups, and hostile state actors. Understanding how social engineering works, recognizing its tactics, and building human-centric defenses are essential components of cognitive warfare and national security.
What Is Social Engineering?
Social engineering is a psychological manipulation technique that induces individuals to divulge confidential information, grant unauthorized access, or take actions that serve an attacker’s objectives. The term encompasses a range of tactics, from simple deception to sophisticated, multi-phase operations that unfold over months or years.
Unlike traditional espionage, which might involve burglary, bribery, or technical surveillance, social engineering attacks require no physical breach. The victim willingly — though unknowingly — provides access, information, or assistance.
In military contexts, social engineering targets:
Military personnel (active duty, reserves, veterans)
Defense contractors and supply chain partners
Government civilians with security clearances
Intelligence community members
Journalists, academics, and analysts with access to sensitive networks or information
The goal may be intelligence collection, system compromise, reputation damage, or operational disruption.
The Psychology of Social Engineering: Why It Works
Social engineering succeeds because it targets fundamental human cognitive and emotional vulnerabilities.
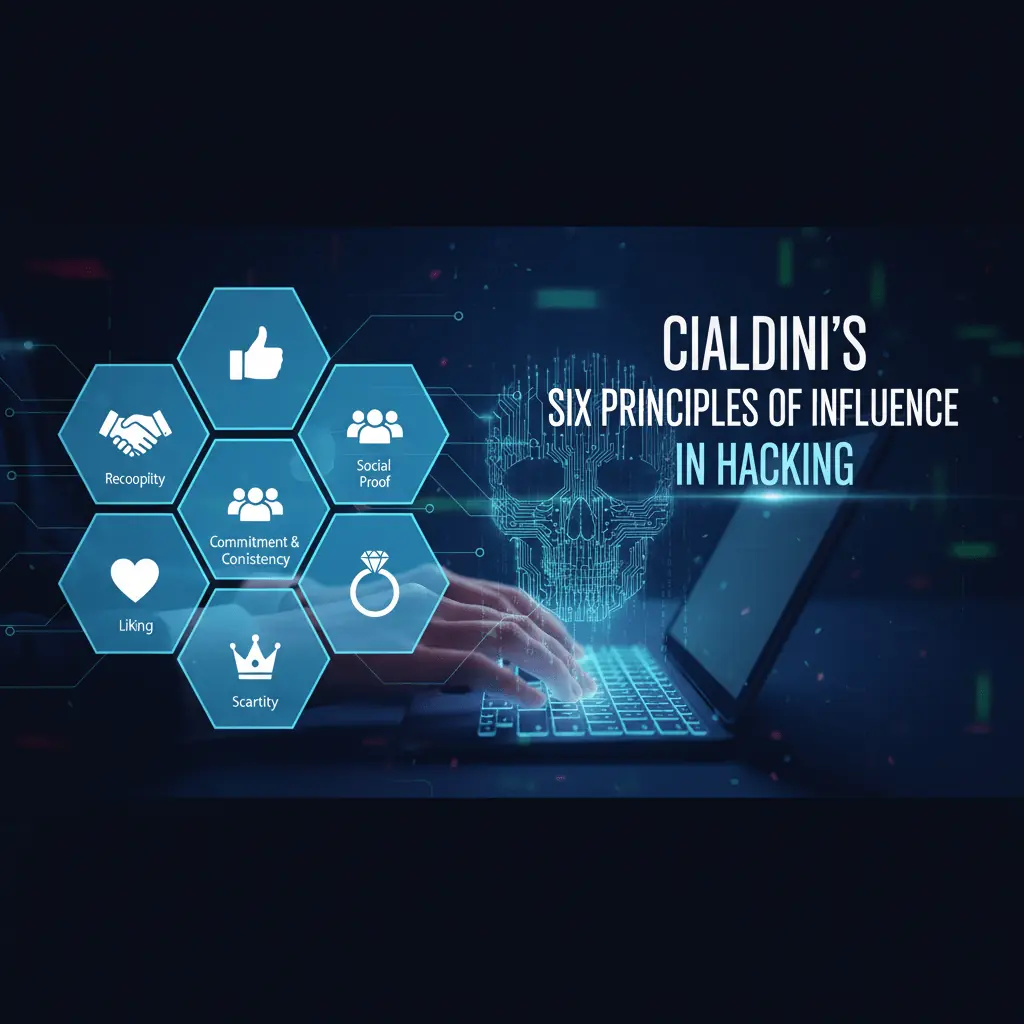
1. Authority Bias
People are conditioned to obey authority figures: bosses, officials, law enforcement, military superiors. Attackers impersonate these roles to compel compliance.
Example: An attacker calls a help desk claiming to be a general’s aide, demanding an immediate password reset. The help desk employee complies because they fear disobeying a senior officer.
2. Liking and Similarity
People are more likely to comply with requests from individuals they like or perceive as similar to themselves. Attackers build rapport, find common ground, and mirror behavior.
Example: An intelligence officer targets a defense analyst by engaging in friendly conversation about a shared hobby at a conference. Over months, the relationship deepens, and the analyst gradually reveals sensitive information.
3. Social Proof
People look to others for guidance on appropriate behavior. If everyone else seems to be complying, the target assumes compliance is normal and safe.
Example: A phishing email claims “all employees have already completed this mandatory training.” The target, seeing the implied consensus, clicks the malicious link.
4. Scarcity and Urgency
People act quickly when they believe an opportunity is limited or a threat is imminent. Attackers create artificial urgency to bypass rational deliberation.
Example: “Your security clearance will be suspended unless you verify your credentials within the next hour.” The target rushes and makes mistakes.
5. Reciprocity
People feel obligated to return favors. Attackers give something small — a compliment, a small gift, helpful information — to create a sense of debt.
Example: An attacker provides a “useful” unclassified report to a target. Later, they ask for a small favor in return. The target complies because refusing feels ungrateful.
6. Fear and Threat Avoidance
Fear overrides rational analysis. Attackers threaten negative consequences — job loss, legal trouble, demotion, public embarrassment — that the target can avoid only by complying.
Example: “Your account has been compromised. If you do not reset your password immediately, your access will be permanently revoked.”
Common Social Engineering Tactics
Phishing
The most prevalent social engineering attack. Attackers send deceptive emails, text messages (smishing), or phone calls (vishing) impersonating legitimate entities — IT support, HR, banking institutions, or colleagues. The message typically urges the target to click a link, download an attachment, or provide credentials.
Military variant: Spear-phishing targets specific individuals using personalized information gathered from open sources (social media, professional profiles, conference attendee lists). A spear-phishing email might reference a real project, conference, or colleague to appear authentic.
Pretexting
The attacker creates a fabricated scenario (pretext) to justify their request for information or access. They research their target extensively, adopting a believable persona — IT technician, journalist, researcher, new employee, or maintenance worker.
Example: An attacker posing as a building maintenance worker arrives at a military facility during a legitimate repair window (learned through open-source scheduling information). A busy guard waves them through without proper verification.
Baiting
Attackers leave physical media — USB drives, external hard drives, or CDs — in locations where targets will find them. The media is labeled enticingly (“Salary Information,” “Classified — Do Not Share”). Curious targets insert the media, which installs malware.
Military variant: USB drives left in parking lots of defense contractor facilities. A well-intentioned employee picks one up, plugs it into their work computer to identify the owner, and unwittingly installs a backdoor.
Quid Pro Quo
The attacker offers a service, benefit, or favor in exchange for information or access. “I’ll fix your computer issue if you provide your login credentials.” “Help me with this small form, and I’ll expedite your clearance process.”
Tailgating (Piggybacking)
An attacker follows an authorized person through a secure door, often carrying heavy boxes or appearing distracted. The authorized person holds the door out of politeness, violating security protocol.
Reverse Social Engineering
A sophisticated, multi-phase attack. The attacker first creates a problem (e.g., disrupting a network service), then presents themselves as the solution (e.g., offering to fix the problem), and finally extracts information or access during the “help” process.
Social Engineering in Military and Intelligence Operations
From a defense perspective, social engineering is a recognized intelligence-gathering tradecraft. Adversary nations, including near-peer competitors, routinely deploy social engineering against military and government targets.
Targeting Process
Reconnaissance: Open-source intelligence (OSINT) collection from social media, professional networking sites, government directories, conference proceedings, and public records. Attackers build detailed profiles: job roles, reporting chains, travel schedules, personal interests, family members, and psychological vulnerabilities.
Weaponization: Crafting the attack vehicle — email, phone call, in-person approach — tailored to the target’s profile. This may involve creating fake social media accounts, registering domain names similar to legitimate organizations, or manufacturing physical credentials.
Delivery: Executing the attack. Phishing emails sent at optimal times (early morning, before holidays). Phone calls during busy periods when targets are distracted. In-person approaches at conferences, hotels, or restaurants.
Exploitation: Extracting information, credentials, or access. This may be a single request or an extended relationship (e.g., a “false flag” recruitment operation).
Exfiltration and Cover: Removing stolen data while erasing evidence of the attack. Attackers may also establish persistence — backdoor access for future operations.
Detecting Social Engineering: Red Flags for Defense Personnel
Training military and government personnel to recognize social engineering is critical. Warning signs include:
Unsolicited contact from someone requesting information, access, or action
Urgency or pressure to bypass normal procedures
Appeal to authority without proper verification (badge, credentials, chain of command)
Too-good-to-be-true offers or unusual requests for assistance
Inconsistencies in stories, credentials, or contact information
Requests to circumvent security protocols (“My badge is lost, just let me in this once”)
Unusual emotional manipulation (making you feel guilty, afraid, or obligated)
Countermeasures: Building Human Firewalls
Individual-Level Defenses
Verify identity: Always confirm credentials through independent channels. Call back using a known number, not the one provided.
Follow protocols: Security procedures exist because of past breaches. Never bypass them for convenience or politeness.
Pause and question: Before complying with any sensitive request, pause. Ask: “Does this make sense? Is there any reason this request might be suspicious?”
Report suspicious contacts: Attempted social engineering is intelligence about adversary tactics. Report it immediately.
Limit personal exposure: Reduce open-source intelligence (OSINT) vulnerabilities by minimizing personal information on professional and social media.
Organizational Defenses
Security awareness training: Regular, scenario-based training on social engineering tactics, including simulated phishing exercises.
Verification protocols: Mandatory two-person or two-channel verification for sensitive requests (e.g., password resets require both email and phone confirmation).
Access controls: Least privilege principle — individuals have only the access necessary for their role, limiting damage from compromised accounts.
Reporting mechanisms: Easy, anonymous, and non-punitive reporting of suspected social engineering attempts.
Red teaming: Regular simulated social engineering attacks to test organizational vulnerabilities and train personnel.
Conclusion
Social engineering exploits the most fundamental vulnerability in any security system: human nature. The tendency to trust, to help, to obey authority, to avoid conflict, and to act under pressure are not character flaws — they are normal psychological features. But in the context of military and national security, these normal features become exploitable weaknesses.
Adversaries know this. They invest heavily in social engineering because it works. It is cheaper than technical hacking, safer than physical infiltration, and often more effective than either. The defense is not to eliminate human nature — that is impossible. The defense is awareness, training, verification protocols, and a culture that treats security as everyone’s responsibility.
In cognitive warfare, the battlefield is the human mind. Social engineering is how the enemy advances across that battlefield without firing a shot. Your ability to recognize, resist, and report is the defensive line.